Python Hill Cipher Encryption Tool
A Python command-line tool that implements the classical Hill cipher using matrix multiplication and modular arithmetic to transform plaintext into encrypted text.
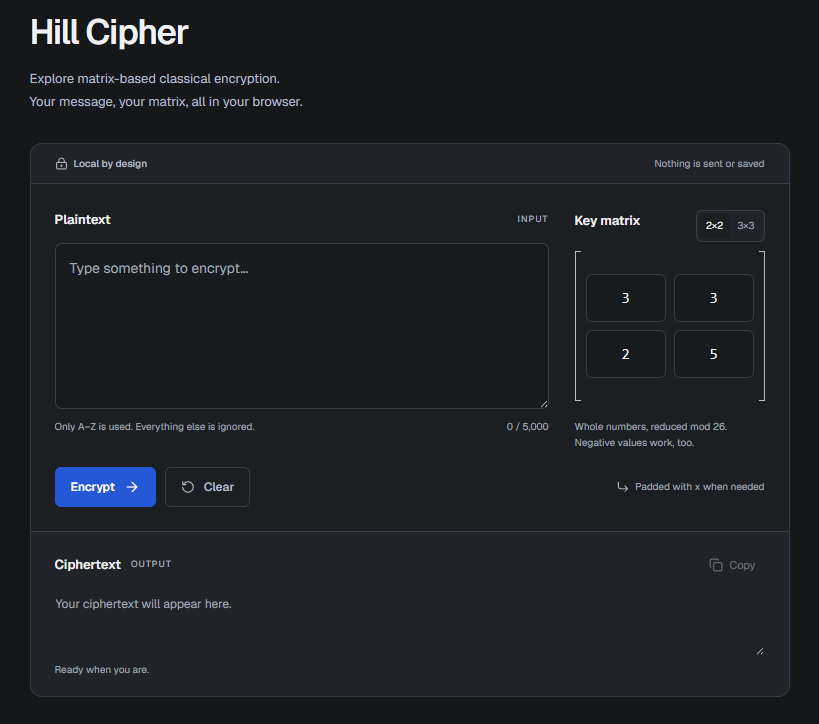
Hill Cipher Encryption Tool
Live Demo: https://hillcipher-ui.vercel.app/ Source Code: https://github.com/ChristopherJacques/HillCipherEncrypt
Overview
The Hill Cipher Encryption Tool is a classical cryptography project I built to implement the Hill cipher algorithm directly rather than relying on an encryption library.
The core implementation accepts a matrix-based encryption key and plaintext file, normalizes the input, converts characters into numerical values, processes the plaintext in fixed-size blocks, performs matrix multiplication modulo 26, and produces the resulting ciphertext.
I also created an interactive browser-based demonstration that makes the algorithm easier to explore without requiring users to run the Python command-line implementation locally.
The project is intentionally focused on understanding the algorithm itself and demonstrates how concepts from linear algebra, modular arithmetic, input validation, and data transformation can be translated into working software.
Problem / Motivation
The goal was to understand how a classical block cipher actually transforms data.
Instead of treating encryption as a black-box library call, I implemented the mathematical process behind the Hill cipher: representing letters numerically, organizing plaintext into vectors, multiplying those vectors by a key matrix, reducing the results modulo 26, and converting the transformed values back into characters.
Building the algorithm directly made the project useful as both a programming exercise and a practical introduction to the relationship between cryptography and linear algebra.
Because the Hill cipher is a historical cryptographic technique rather than a secure modern encryption standard, the project is intended for educational and demonstrative use rather than protection of sensitive information.
Core Features
File-Based Plaintext Processing
The command-line implementation accepts plaintext from an external UTF-8 text file rather than relying on hard-coded input.
Before encryption, the program:
- retains ASCII alphabetic characters
- removes unsupported characters
- normalizes letters to lowercase
- validates that usable plaintext remains
- limits raw plaintext input to 5,000 characters
- automatically pads incomplete blocks with
x
This produces predictable input for the cipher's matrix operations while preventing malformed or excessively large input from reaching the encryption routine.
External Encryption Key
Encryption keys are provided through a separate text file.
The application supports:
- 2×2 key matrices
- 3×3 key matrices
- signed integer values
- automatic modulo-26 normalization
The parser validates the declared matrix dimension, number of rows, number of values per row, and integer formatting before the key is accepted.
Keeping the encryption key external makes the implementation reusable across different matrices without changing the source code.
Ciphertext Generation
After preparing the plaintext, the program separates it into blocks matching the dimensions of the selected key matrix.
Each block is converted into a numerical vector using the mapping:
a = 0 through z = 25
The program then:
- multiplies each plaintext vector by the key matrix
- reduces each resulting value modulo 26
- converts the resulting numerical values back into letters
- combines the transformed blocks into the final ciphertext
The resulting ciphertext is printed directly to the terminal and formatted for readable output.
Interactive Demonstration
In addition to the Python command-line implementation, the project includes a live browser-based demonstration of the Hill cipher workflow.
The interactive version provides a more accessible way to experiment with the algorithm and observe how plaintext and matrix keys produce ciphertext without requiring a local Python environment.
Live Demo: hillcipher-ui.vercel.app
Standout: Matrix-Based Encryption
The most important part of the project is the implementation of the actual Hill cipher transformation.
Unlike a simple substitution cipher that transforms individual characters independently, the Hill cipher operates on groups of characters simultaneously.
For a plaintext vector p and key matrix K, the transformation can be represented as:
c = K × p mod 26
I implemented this process directly in Python:
- normalize plaintext
- pad the plaintext to the required block size
- convert characters into numerical values
- organize the values into vectors
- multiply each vector by the key matrix
- apply modulo-26 arithmetic
- convert the results back into letters
This demonstrates the direct relationship between cryptographic transformations, matrix operations, and modular arithmetic.
Standout: Input Validation and Normalization
The mathematical transformation depends on predictable input, so the current implementation performs validation before encryption begins.
The application validates key dimensions and structure, rejects malformed integers, limits input sizes, ensures plaintext contains valid ASCII letters, and automatically pads plaintext when its length does not match the selected block size.
Separating validation, normalization, padding, encryption, and output formatting makes the implementation easier to understand while reducing unexpected behavior from malformed input.
Technical Implementation / Approach
The core application is a deliberately small Python command-line program.
Plaintext and key files are loaded from disk, while Python handles validation, normalization, padding, matrix calculations, modulo arithmetic, and output formatting.
The current implementation performs the matrix operations directly with Python rather than depending on a numerical computing library.
The main encryption routine:
for offset in range(0, len(padded), size):
    vector = [
        ord(char) - ord("a")
        for char in padded[offset:offset + size]
    ]

    for row in matrix:
        value = sum(
            entry * letter
            for entry, letter in zip(row, vector)
        ) % 26

        ciphertext.append(chr(value + ord("a")))
This keeps the core mathematical transformation visible in the source code rather than abstracting it behind a cryptographic or matrix-processing library.
The command-line implementation prints the normalized key, normalized plaintext, padding count, and resulting ciphertext to the terminal.
Architecture / Tech Stack
Core Language: Python 3.9+
Interactive Demo: Next.js, TypeScript
Deployment: Vercel
Python Dependencies: Standard library only
Input / Output: UTF-8 text files and command-line output
Important Logic / Algorithms:
- Hill cipher
- matrix multiplication
- block-based encryption
- character-to-integer mapping
- modulo-26 arithmetic
- plaintext normalization
- automatic block padding
- key matrix validation
Summary
- Implemented the Hill cipher transformation directly rather than relying on an encryption library.
- Translated matrix multiplication and modulo-26 arithmetic into a working encryption routine.
- Added automatic plaintext padding for 2×2 and 3×3 matrix dimensions.
- Implemented structured validation for key files, plaintext, matrix dimensions, and malformed input.
- Added bounded file processing and clear command-line error handling.
- Kept the Python implementation dependency-light by using only the standard library.
- Built a live interactive demonstration so the algorithm can be explored directly from a browser.
- Maintained a clear distinction between classical cryptography education and modern production-grade encryption.